- 1Create a free account
- 2Pick your topics and platforms
- 3Read your tailored feed
- 4Ask the CMMCSimple Assistant
Get the feed your contracts depend on
Create a free account, pick your topics, and see your tailored compliance feed today.
Stay ahead of CMMC and DoD cybersecurity developments with AI-powered news aggregation, personalized updates, and source-backed answers.
Guidance
Guide: What Are ODPs in NIST 800-171 Rev 3?The shift from NIST SP 800-171 revision 2 to revision 3 includes a lot of changes, which we've already covered from a bird's-eye view over in this post. One of the biggest changes in Rev 3 is the introduction of ODPs, or Organization-Defined Parameters. These...
Ignyte Platform Blog · Oct 30, 2026
Ecosystem
CMMC Accreditation Body Endorses Pentagon’s Proposed Implementation Changes in CMMC 2.0 - November 04, 2021The Cyber AB — Training, Certification & Press
CMMCAudit.org — CMMC Audit Preparation · Oct 27, 2026
Federal News Network · Oct 26, 2026

PreVeil (LinkedIn)
Cyber AB Town Halls · Oct 31, 2026
Chat in plain English and get answers grounded in the latest coverage, with source links. No account needed to try it. News awareness only, not legal or compliance advice.
Cyber News
Dark Reading · Nov 12, 2026
Defense News
The missiles — which are yet to be manufactured — are not expected to be delivered until a couple of years into the 2030s.
Defense News · Nov 2, 2026
Cyber News
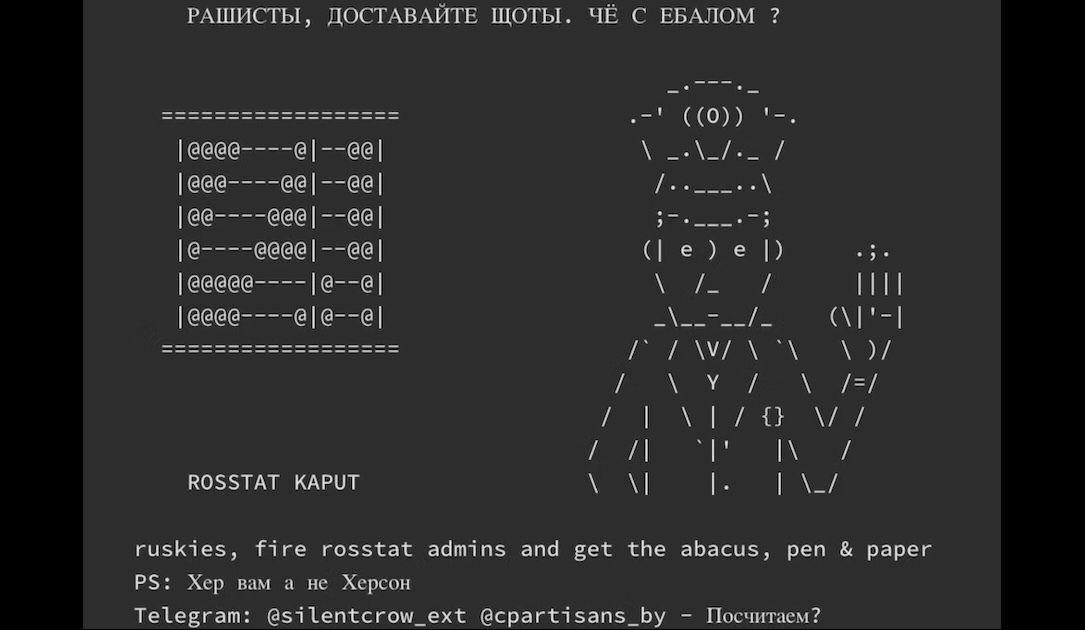
An alliance of Belarusian and pro-Ukrainian hackers claimed to have taken out Russia's federal statistics agency, Rosstat, and stolen vast amounts of sensitive government data in a cyberattack.
The Record · Nov 2, 2026

Defense News
The purchase, arranged via a government-to-government agreement between Greece and Portugal, covers three KC-390 aircraft with options for up to six manufactured by Brazilian planemaker Embraer.
Breaking Defense · Nov 2, 2026
Federal Policy
The group wants independent patient safety reviews and fixes at facilities already using Oracle Health before VA moves ahead with more deployments.
Government Executive · Nov 2, 2026
Defense News
The new concept has sent personnel from Cyber Defense Command at Fort Meade to the Pacific theater.
Breaking Defense · Nov 2, 2026
Defense News
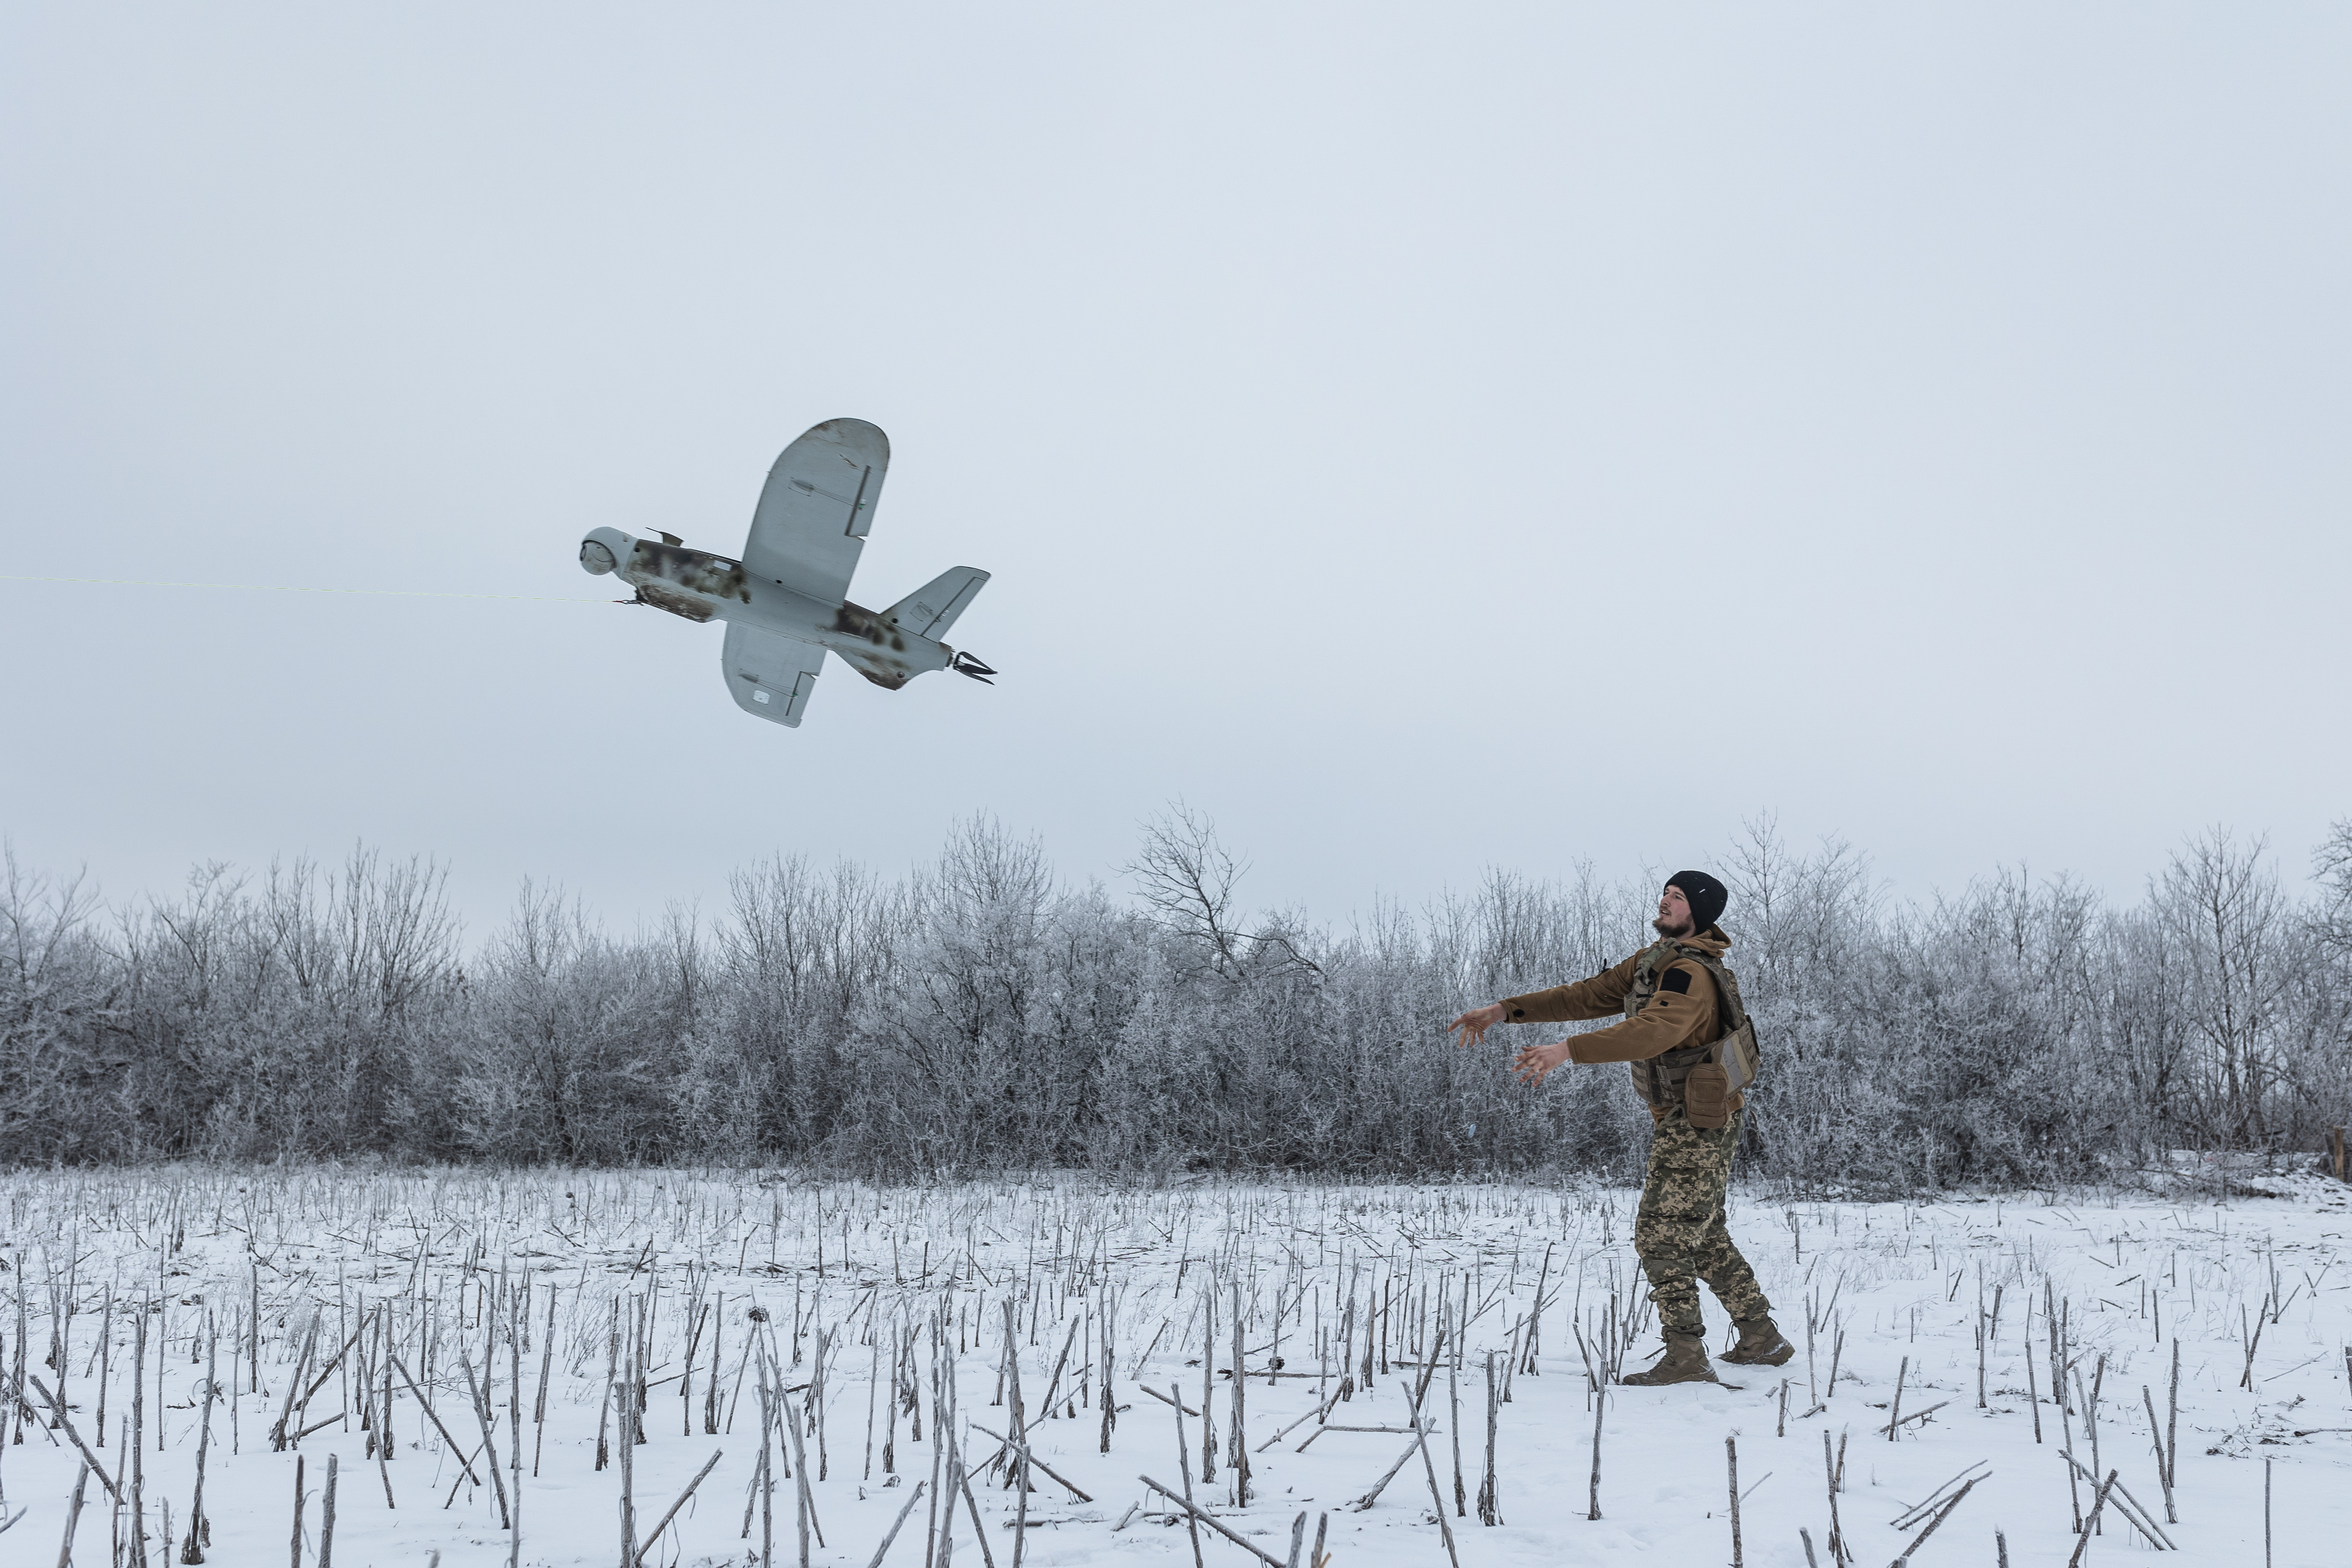
A small new receiver can co-opt video from Russian unmanned systems, allowing Ukrainian drone operators to intercept enemy live feeds in real time, the device's makers said this month.
Defense News · Nov 2, 2026
DoD
ODENTON, Md. – The 780th Military Intelligence Brigade (Cyber) hosted a computer challenge event for young people, known as Hackathon VI, to encourage teen interest in STEM (science, technology, engineering, and mathematics) at the Odenton Library, Anne Arundel County Public Library, on October 29. The October event attracted 54 young people, and not including their parents, it was the most the brigade has ever hosted since the unit started the computer challenge event in 2019.
DVIDS · Nov 2, 2026
Cyber News
CISA added two new Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527) to its Known Exploited Vulnerabilities catalog on Friday, after Ivanti updated an earlier security advisory with details about the flaws. Three flaws chained to gain a foothold CVE-2026-111357, a missing authentication for a critical function vulnerability that allows a local authenticated attacker to escalate their privileges, and CVE-2026-118527, a “Generation of Predictable Numbers or Identifiers Vulnerability” that makes remote authenticated file upload possible, have been
Help Net Security · Nov 2, 2026

Cyber News
Google shut down the servers behind XCPE, a backdoor hidden in the firmware of Android TV set-top boxes. Google’s Threat Intelligence Group attributes the operation with high confidence to Videostrong Technology, the company that manufactured many of those boxes. More than 1.3 million devices were enrolled. XCPE malware overview (Source: Google) Access The business model was access. Researchers say the company sold entry to its customers’ living rooms to criminal affiliates, who pushed their own
Help Net Security · Nov 2, 2026

Cyber News
A botnet of more than 1.3 million Android devices, mostly TV set-top boxes, lost control of its servers in late October in a takedown led by Google. Google says it is highly confident that device maker Videostrong intentionally put a backdoor in the boxes and sold access to criminals. They used the boxes for ad fraud and to pass other people's internet traffic through owners' home
The Hacker News · Nov 2, 2026
DoD
Interagency partnerships and proactive planning took center stage at this year’s Minnesota Digital Government Summit in August, where military and local government technology leaders gathered to discuss strategies for collaborative network defense.The event brought together public sector leaders from state, local, and territorial governments from across Minnesota regarding all things IT and cyber. Cyber security, digital transformation, cloud services, AI – it’s all hyper relevant in how governments across the state are able to provide essential services to their citizens, and provenance for our modern way of life.
DVIDS · Nov 2, 2026

Cyber News
The maintainer of BTCPay Server, an open-source cryptocurrency payment processor, has urged users to install the latest version as hackers have been draining "hot wallets" on instances running older versions.
BleepingComputer · Nov 2, 2026
Federal Policy
Sources say federal oversight of the Swiss cybersecurity firm spanned multiple administrations before culminating in last week's DHS removal order.
Nextgov/FCW · Nov 2, 2026
Cyber News
Mobile carriers can retain years of call and text metadata, exposing sensitive details about customers' relationships, locations, and daily routines if breached. Cape examines the privacy risks of long-term telecom data retention and how its mobile service reduces exposure by automatically deleting call records.
BleepingComputer · Nov 2, 2026
Cyber News
Significant cybersecurity deals were announced by Absolute Security, Aikido, Anthropic, Cohere, Hex-Rays, and Proofpoint.
SecurityWeek · Nov 2, 2026
DoD
The War Department's Office of Strategic Capital announced a conditional loan commitment of up to $450 million to Neros Inc., a U.S.-based developer and manufacturer of dual-use small unmanned aircraft systems.
DoD News Releases · Nov 2, 2026
Cyber News
The latest "Digital Defense Report" identifies government agencies as prime targets for AI attacks but doesn't mention that they are broadly being targeted through Microsoft bugs.
Dark Reading · Nov 2, 2026
Threat Intelligence
Last week, an often-ignored&#;x26;#;xc2;&#;x26;#;xa0;TCP option, introduced in 2020, made the news due to a new vulnerability in Linux&#;x26;#;39;s implementation (RFC&#;x26;#;xc2;&#;x26;#;xa0;8684, &#;x26;#;xc2;&#;x26;#;xa0;CVE-2026-98432)
SANS Internet Storm Center · Nov 2, 2026

Defense News
From vehicles to wearable drone detection, new soldier systems were on display at AUSA 2026. Check out a roundup of our social coverage.
Defense News · Nov 2, 2026
Cyber News
A new Windows infostealer sends the data it steals to an AI model and asks it to rank the victim’s assets by how much money they could bring in, Cisco Talos has found. “There is a new idea in the cybercrime world — cast a wide net, steal everything, and let AI sort out the specifics,” said Ryan Fetterman, a security researcher at Cisco. The malware calls itself VOLTA-AUTODOXER and turned up through Talos’ CAIRN
Help Net Security · Nov 2, 2026

Cyber News
Cybersecurity researchers have disclosed details of a cyber espionage campaign targeting Israel and the Kurdistan Region of Iraq by an Iran state-aligned threat actor between August and October 2026. According to a report published by Dream Research Labs, the campaign has led to the compromise of a high-profile individual in Israel, along with additional compromises affecting a government cloud
The Hacker News · Nov 2, 2026
Cyber News
Armadin found 88% of critical and high findings in its client tests fell outside vendor advisories
Infosecurity Magazine · Nov 2, 2026

Cyber News
The Florida Department of Education says SSNs and other personal data may have been exposed in a breach of its financial aid website.
SecurityWeek · Nov 2, 2026

Defense News
From industry stalwarts to small startups, defense tech creators are looking to provide solutions as conflict morphs on a monthly basis. See some of what they had to offer at AUSA 2026.
Defense News · Nov 2, 2026
Cyber News
Apple does not attribute attacks or the notices to specific malicious actors or geographical regions, the notification said, due to the “extreme cost, sophistication, and worldwide nature of mercenary spyware attacks [which] make them some of the most advanced digital threats in existence today.”
The Record · Nov 2, 2026

Defense News
As the American military seeks new capabilities and advanced systems amid rapid change, defense companies of all sizes showcased their solutions at a major defense conference.
Defense News · Nov 2, 2026
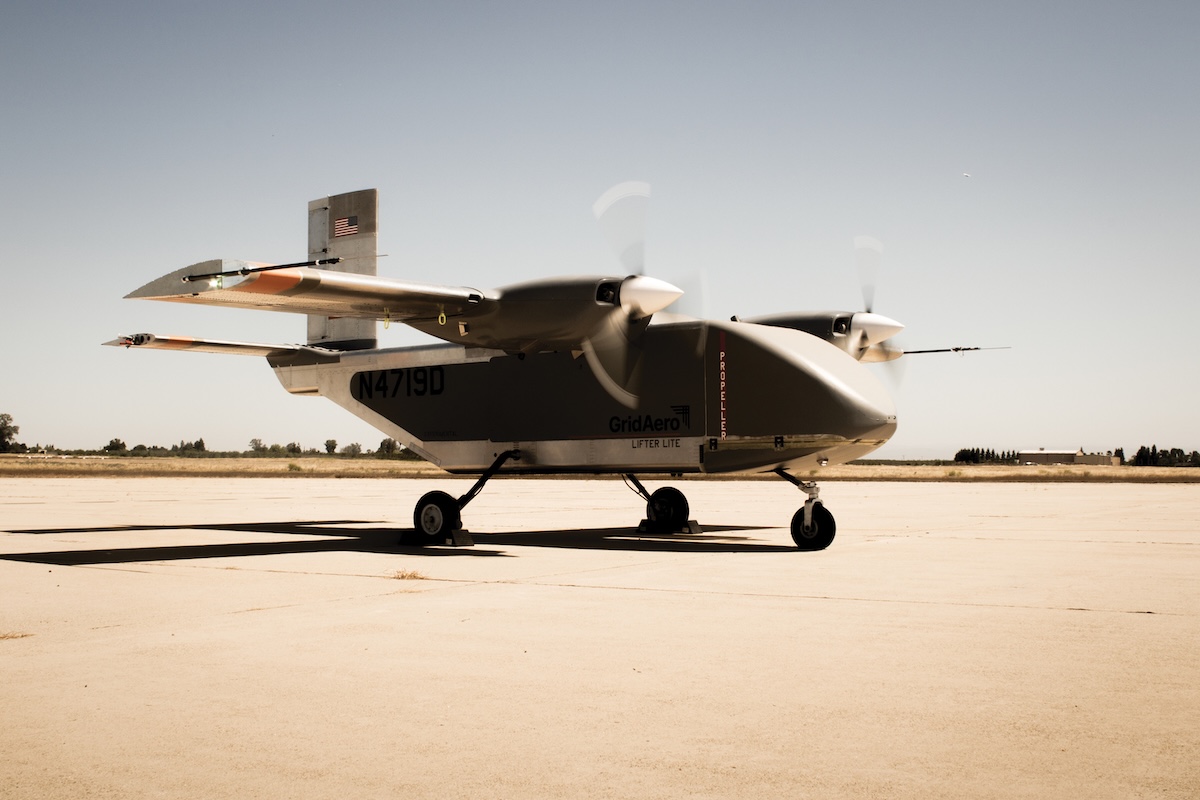
Defense News
Oshkosh Defense partnered with Grid Aero to scale production of the Lifter aircraft, marking the defense giant's first foray into aircraft manufacturing.
Defense News · Nov 2, 2026

Cyber News
A popular Ukrainian air raid alert system was hacked over the weekend, prompting a cyber group to breach a similar Russian system in retaliation.
The Record · Nov 2, 2026

Cyber News
A cyberattack on refrigeration systems has disrupted stores run by multiple supermarket chains across several European countries after hackers remotely changed temperature settings on freezers and cooling systems.
BleepingComputer · Nov 2, 2026
Cyber News
Three weeks after the attack that turned refrigeration units in French supermarkets into ovens overnight, similar cyberattacks have hit shops in other European countries and again caused refrigerated food to be spoiled. Belgium, Luxembourg and Sweden affected “[In Belgium,] fridges and freezers have been affected at Delhaize, Carrefour and Spar, among others. The attackers remotely switched the units’ evaporators to defrost mode, causing the fridges to warm up,” Belgian news agency Belga reported today. “The
Help Net Security · Nov 2, 2026
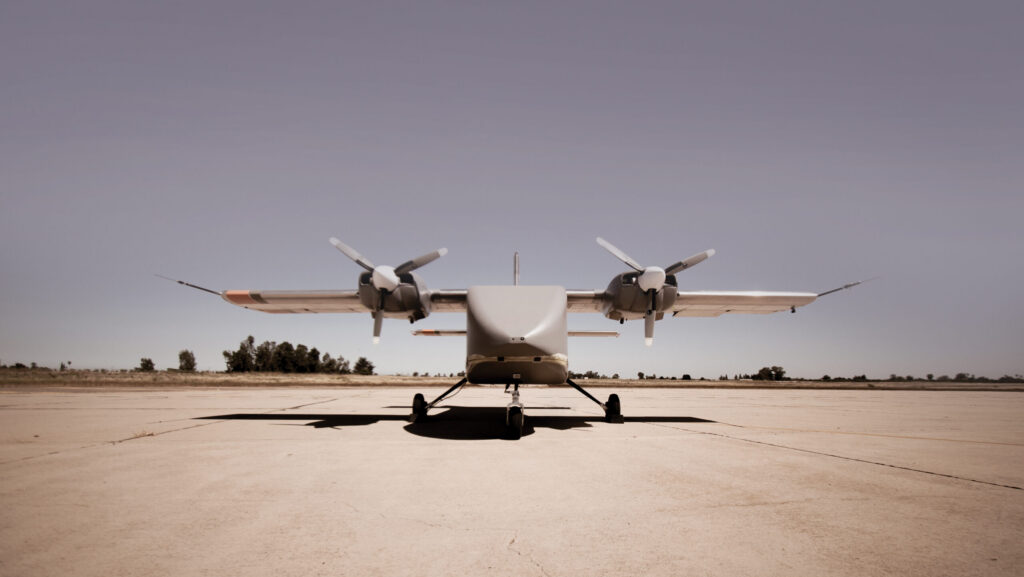
Defense News
The two companies plan to team up on “design for manufacturability, production planning, supply chain optimization, and ultimately building Lifter aircraft at scale.”
Breaking Defense · Nov 2, 2026
Federal Policy
The deadline for submissions is Dec. 31, 2026.
Nextgov/FCW · Nov 2, 2026
Cyber News
Researchers have tracked the increased use of Artex and other frameworks in order to automate and speed up attack methods.
Cybersecurity Dive · Nov 2, 2026
Cyber News
Organizations in the region face attacks from the known India-linked threat group, which leverages legitimate Windows functionality in three distinct attack chains.
Dark Reading · Nov 2, 2026

Defense News
Building good credit is often easier than you think — follow these tips for getting back on track.
Defense News · Nov 2, 2026

Defense News
International weapons makers step forward with new interceptors and deals for armored vehicles, while an American company secures a fighter contract.
Defense News · Nov 2, 2026
Cyber News
Bitter used three infection chains against South and Southeast Asian targets, one with no malware executable
Infosecurity Magazine · Nov 2, 2026
Government Contracting
The tribally-owned contractor says the Small Business Administration suspended it over a single YouTube video and has yet to produce any evidence of wrongdoing a year later.
Washington Technology · Nov 2, 2026
Cyber News
Microsoft has resolved a known issue that prevented some users from activating the Smart App Control security feature after installing the October 2026 KB5127648 Windows 11 security update.
BleepingComputer · Nov 2, 2026

Cyber News
Hackers accessed its online shopping platform and stole customers’ personal and payment card information.
SecurityWeek · Nov 2, 2026

Cyber News
The top payout is for high-impact architectural research demonstrating full administrative control.
SecurityWeek · Nov 2, 2026

Cyber News
Without the cybersecurity agency, experts said, the new group could stumble as it tries to work with critical infrastructure operators on AI security.
Cybersecurity Dive · Nov 2, 2026
Cyber News
Supermarket and grocery store refrigerators across Europe appear to have been hacked early Monday — the second such incident in recent weeks where attackers have manipulated temperature controls and caused stock to spoil.
The Record · Nov 2, 2026
Cyber News
A Trezor Safe 5 sold by CryptoBilis, the reseller linked to the recent Ledger wallet drains, may contain a hidden implant that steals the owner’s recovery phrase, Trezor has warned. Trezor is a Czech company and part of SatoshiLabs Group. It has made hardware wallets since 2014, and its current models are the Safe 3, Safe 5 and Safe 7. “If you bought a Trezor from CryptoBilis from March 2026 onwards and are using it
Help Net Security · Nov 2, 2026

Cyber News
Over 1,000 Internet-exposed GitLab servers are still unpatched against a maximum-severity flaw actively exploited in remote code execution attacks.
BleepingComputer · Nov 2, 2026

Cyber News
Cryptocurrency Exchange Binance blamed a compromised DevOps laptop for the loss of $6.3 billion in cryptocurrency last week, adding that it will now cover any losses faced by its customers. “Binance will cover all losses from the Secure Assets Fund for Users (SAFU) and the company’s funds,” the world’s largest cryptocurrency exchange said in an update on Friday, adding that user funds are safe and that it had found no evidence of wallet private-key leakage during its investigation of the incident. It had frozen approximately $3 billion in assets on-chain, temporarily suspending withdrawals while security checks were completed, and revoking the affected address authorization. Withdrawals are now being restored in phases, initially reopening services across 15 networks, including Bitcoin, Ethereum, Solana, and XRP. Binance says it has replenished approximately 95% of the affected assets using company funds, while the remaining 5%, comprising less-liquid tokens, could take longer to source. The exchange said its preliminary investigation pointed to a compromised employee device that enabled access to a service container involved in withdrawals. “This attack, reportedly on a developmen
CSO Online · Nov 2, 2026
Cyber News
A comment : 3% of ‘critical’ software security bugs, in all of recorded history, have been found in the last month. This is on pace to find another ~100,000 bugs this year alone, adding ~26% more vulnerabilities to the all time total Do you realize how fucking insane that is? Yes. It is a new world out there.
Schneier on Security · Nov 2, 2026
NIST
The guide is designed to help solopreneurs prioritize and implement a selection of actions from the NIST Cybersecurity Framework that would best help their businesses.
NIST News (general) · Nov 2, 2026
Create a free account, pick your topics, and see your tailored compliance feed today.
Want to publish your news with CMMCSimple? Contact us at news@cmmcsimple.com.
Our RSS source list is reviewed and updated every two weeks on Friday, so newly accepted feeds appear with the next update.
© 2026 CMMCSimple